docker compose up -d
Self-Hosted Security Tools
Defensive infrastructure for internet-facing services: intrusion prevention that bans hosts after failed logins, web application firewalls, private certificate authorities, and code and container scanning.
19 apps in this category
Arkime: Full Packet Capture You Can Actually Search Captures and indexes network traffic at scale, storing full packets alongside searchable session metadata so you can find and download the exact traffic you need weeks later.
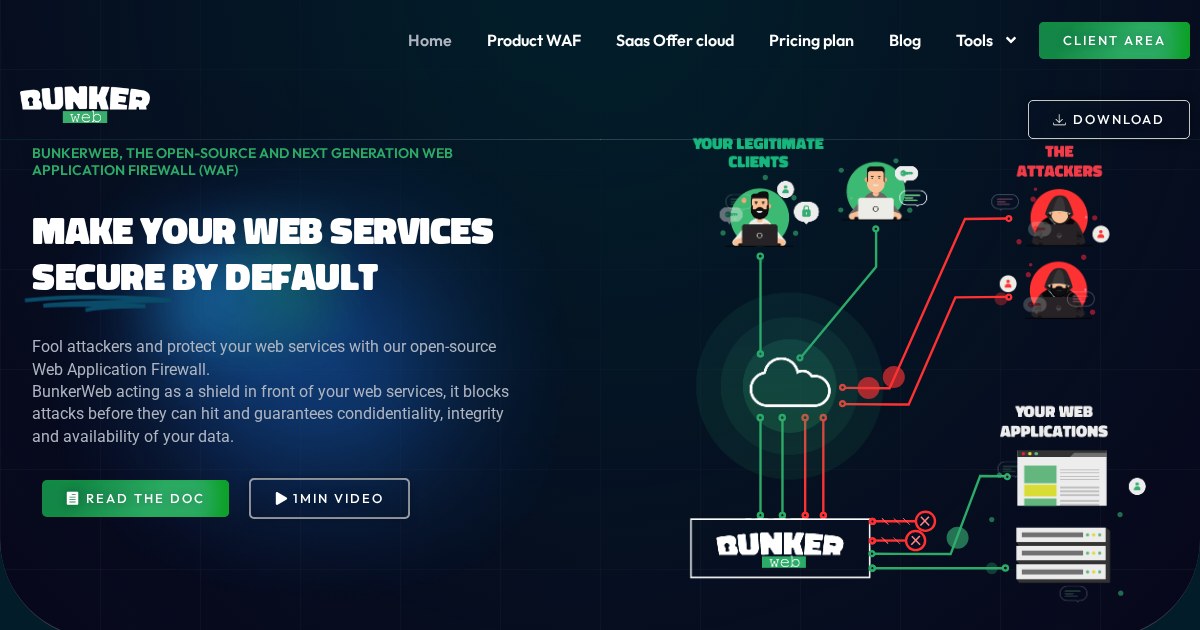
BunkerWeb: Next-generation and open-source web application Next-generation and open-source web application firewall.
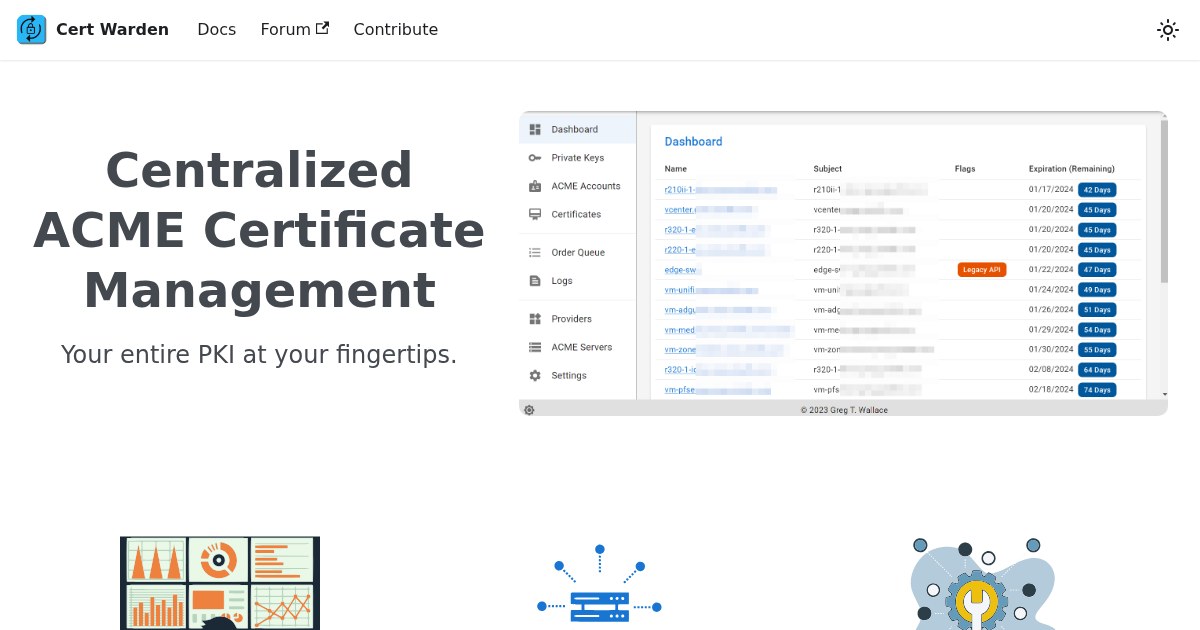
Cert Warden: Centralized certificate management for secure infrastructure Centralized certificate management for secure infrastructure.
CrowdSec: Open-source and participative security solution Open-source and participative security solution offering crowd-sourced protection against malicious IPs.
DefectDojo: Managing Findings From Every Security Scanner Aggregates output from more than a hundred security tools into one place, deduplicating findings across scans and tracking them through triage and remediation.
Fail2Ban: Daemon to ban hosts that cause multiple authentication errors Daemon to ban hosts that cause multiple authentication errors.
Gitleaks: Finding Secrets Before They Reach a Repository Scans code and Git history for hardcoded credentials, API keys, and tokens, runnable as a pre-commit hook so secrets are caught before the commit rather than after the leak.
Greenbone Community Edition: Network Vulnerability Scanning The open-source vulnerability scanner formerly known as OpenVAS, probing hosts on your network for known vulnerabilities, misconfigurations, and exposed services.
Grype: Vulnerability Scanning for Images and Filesystems A focused vulnerability scanner from the Anchore project that pairs with Syft for SBOM generation, scanning container images and directories against known vulnerability data.
Infisical: Secrets Management With a Usable Interface An open-source secrets platform with a web UI, CLI, and integrations for injecting secrets into applications, plus secret scanning to catch credentials before they reach a repository.
Lynis: Auditing a Linux System's Hardening A shell-based security auditing tool that inspects a running system against hundreds of checks and produces a prioritised list of specific hardening suggestions.
OpenBao: Secrets Management, Openly Governed A community fork of HashiCorp Vault under the Linux Foundation, providing encrypted secret storage, dynamic credentials, and encryption as a service with an unchanged Mozilla Public License.
SonarQube: Code quality and security solution with deep Code quality and security solution with deep integration for enterprise environments.
step-ca: Online certificate authority for secure, automated Online certificate authority for secure, automated certificate management.
Suricata: Network Intrusion Detection and Prevention Inspects network traffic against signature rules to detect and optionally block malicious activity, with protocol analysis, file extraction, and TLS metadata logging.
Syft: What You Need to Know: CLI tool for generating a software bill of materials from container images CLI tool for generating a software bill of materials from container images.
Trivy: Scanning Containers, Filesystems, and Code for Known Vulnerabilities A single scanner covering container images, filesystems, Git repositories, Kubernetes clusters, and infrastructure as code, checking dependencies against vulnerability databases and finding leaked secrets.
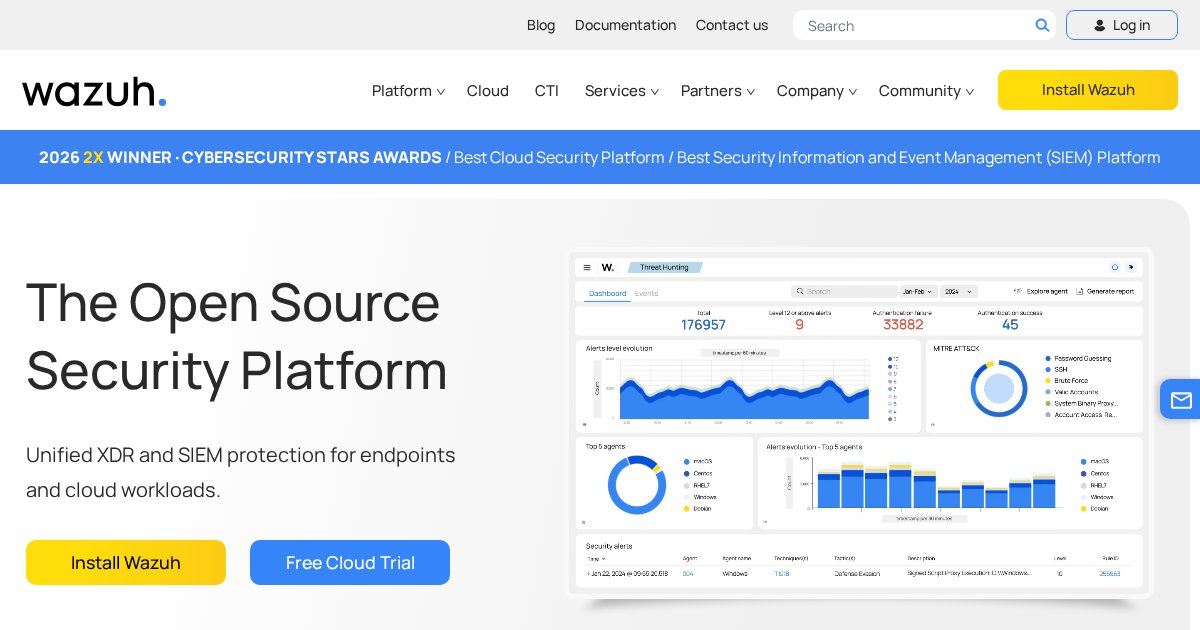
Wazuh: Open Source SIEM and Host Intrusion Detection Agents on each machine collect logs, monitor file integrity, check configuration against benchmarks, and detect intrusions, reporting to a central server with dashboards and alerting.
Zeek: Turning Network Traffic Into Structured Logs Formerly Bro, a network analysis framework that produces detailed structured logs of every connection, DNS query, TLS handshake, and file transfer, with a scripting language for custom analysis.
Browse other categories
Notes & Wikis (47) Media Servers (56) Reading & RSS (51) Music (32) Communication (54) Downloads (28) Networking & VPN (38) Monitoring (34) Productivity (45) Photos (21) Containers (36) File Sync (31) CMS & Websites (23) Recipes & Health (20) Home Automation (17) Development (30) Passwords (11) Auth & SSO (14) Analytics (12) Databases (16) Ad Blocking (10) Dashboards (14) Backup (10) Finance (16) Automation (8) Games (9) AI & ML (28)